Adana TechnologiesLABS
CYBERLive demo

ThreatReady

Threat intelligence you can act on: what is being exploited, which of your systems are exposed, and what to do first.

ThreatReady matches live threat feeds and known-exploited vulnerabilities to your own systems and alerts, ranks what to fix and triage first, and tracks every incident through to lessons learned.
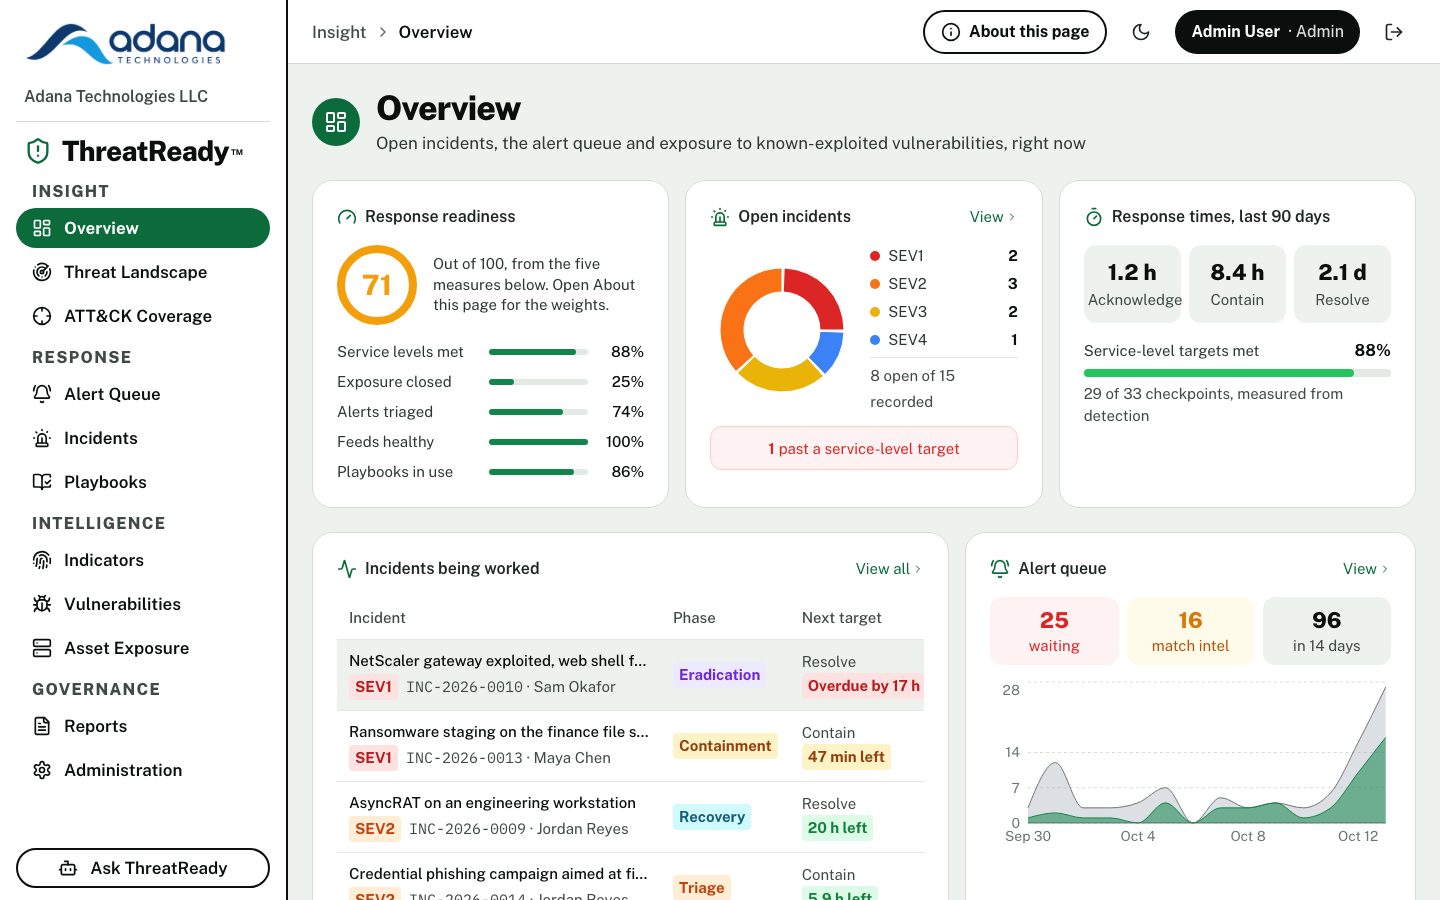
ThreatReady overview with a readiness score, open incidents, response times and the alert queue

THE PROBLEM

Plenty of alerts. Not enough answers.

Security teams receive more threat reports, advisories and vulnerability notices than they can read, let alone act on.

Most of it is generic. It does not say which of your systems are affected, or which alert deserves attention first.

The question that matters is simple: of everything out there, what affects us, and what should we do first?

HOW IT WORKS

From noise to next steps in three moves

  1. 01

    Collect

    Eight public feeds, including CISA's known-exploited catalog, EPSS and MITRE ATT&CK, refresh on a schedule.

  2. 02

    Match

    Indicators and vulnerabilities are matched to your systems and alerts, and scored so the riskiest come first.

  3. 03

    Respond

    Each incident follows a playbook from triage to lessons learned, with tasks, a lead and response-time targets.

INSIDE THE PILOT

What you see in the demo

01

See what the threat feeds are saying

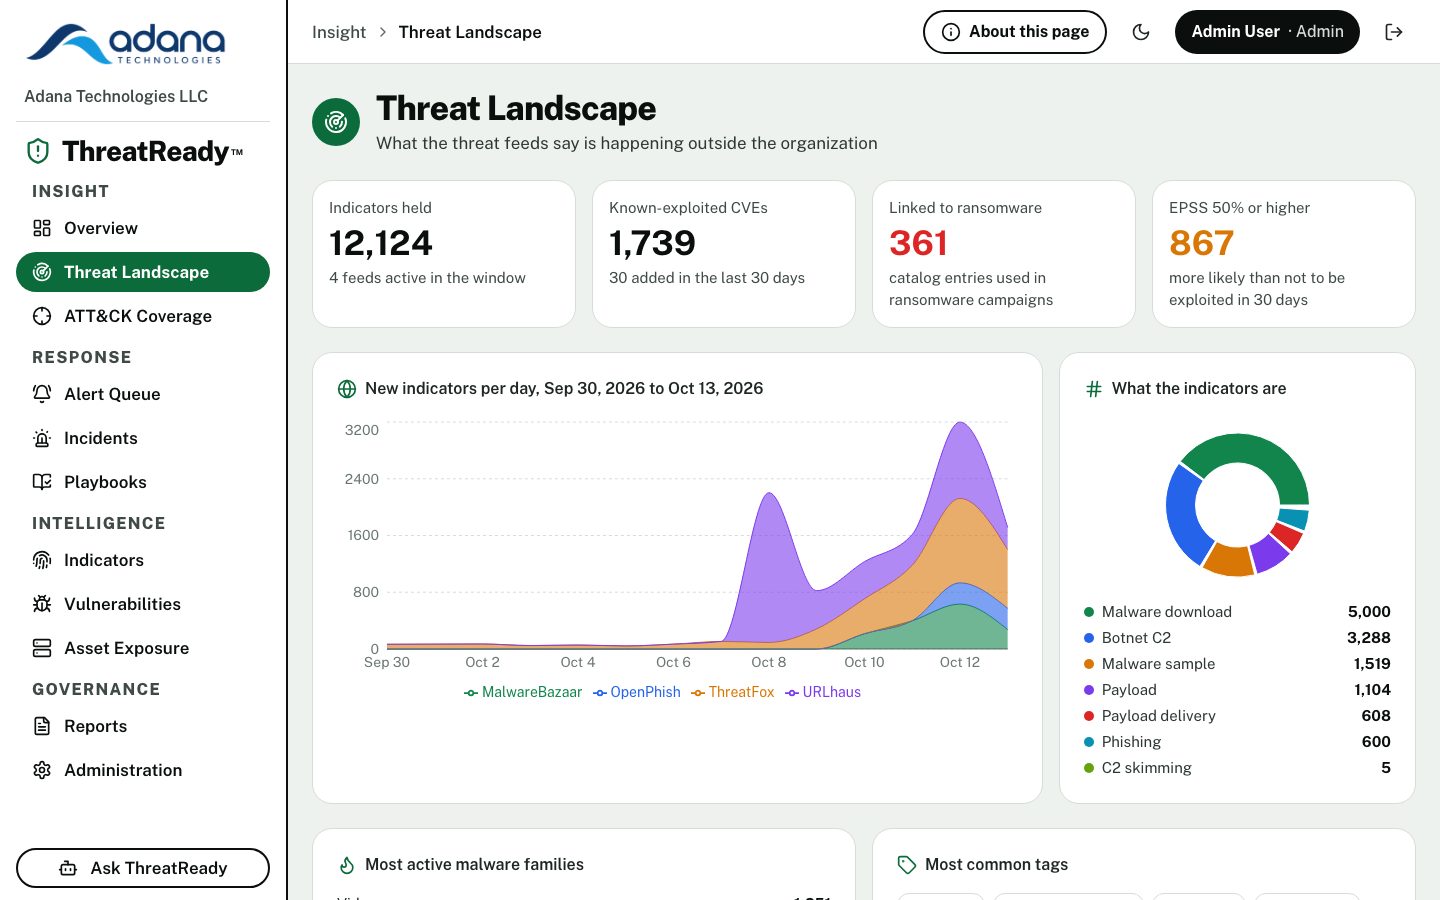
New indicators per day, the most active malware families and the vulnerabilities being exploited now, drawn from public feeds.

Threat Landscape page with indicator counts and a chart of new indicators per day

02

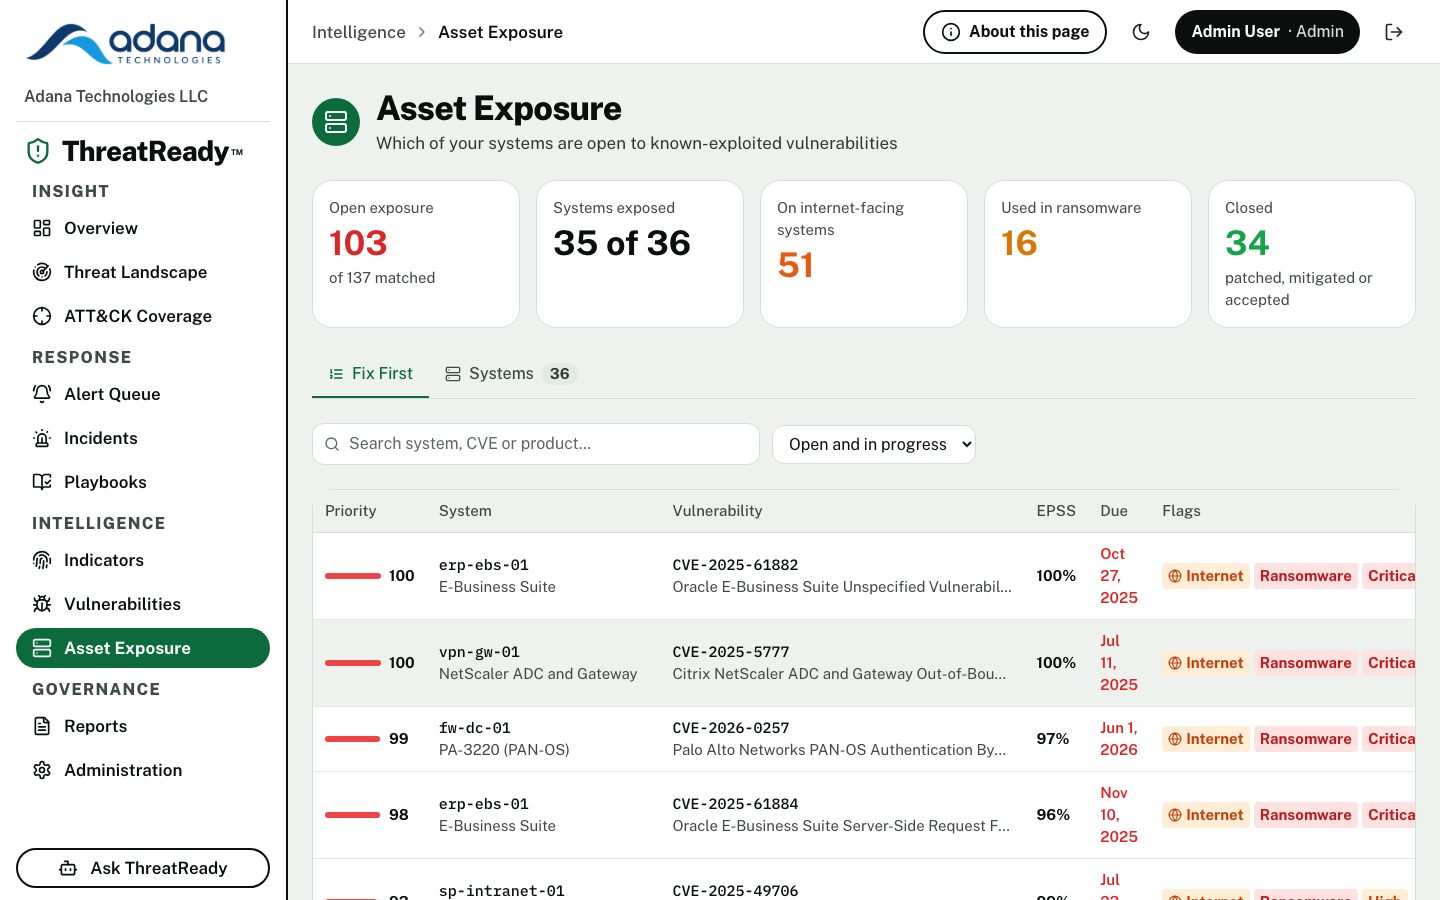
Know which vulnerabilities apply to you

Known-exploited vulnerabilities matched to the products you run, ranked by exploit likelihood, exposure and criticality.

Asset Exposure fix-first list with priority, system, vulnerability and due date

03

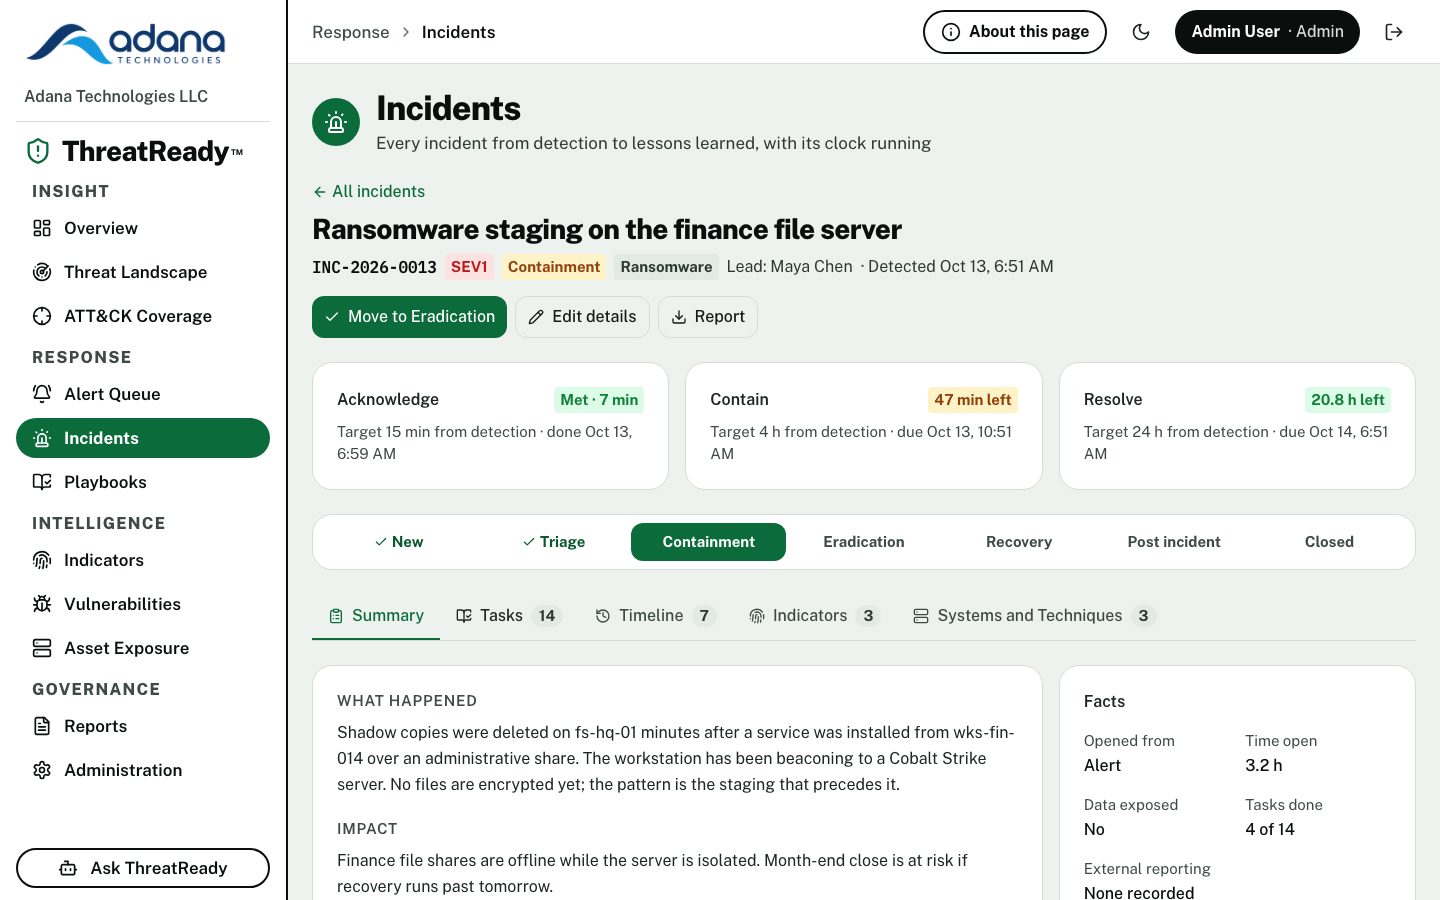
Run the response with the clock in view

Each incident moves through set phases with a playbook of tasks, a timeline, and targets for acknowledging, containing and resolving it.

Incident page showing its phases, response-time targets and summary

04

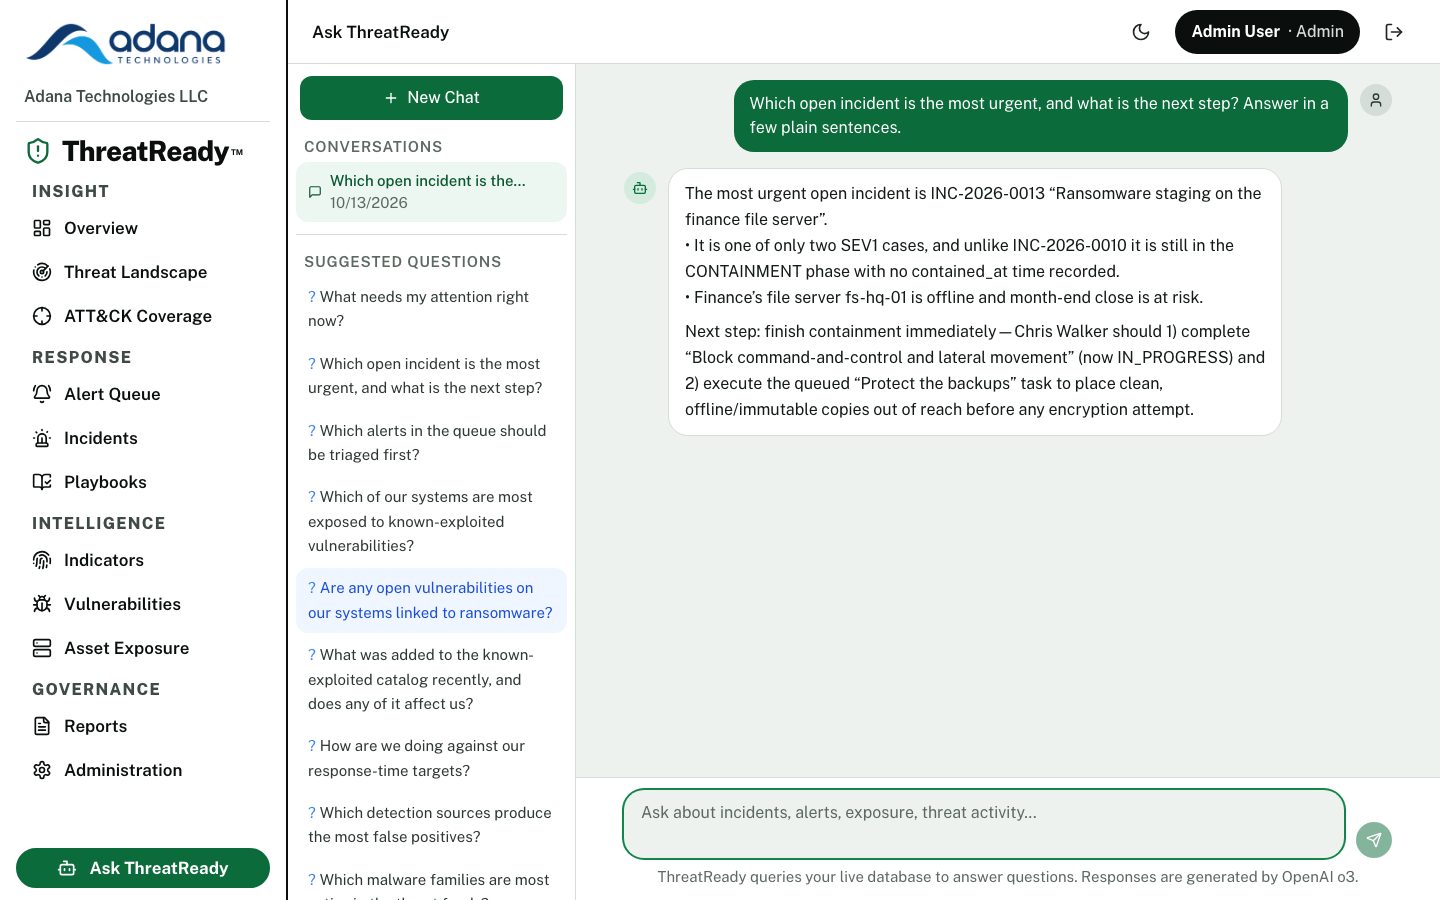
Ask the analyst in plain English

A built-in AI assistant answers from your live incidents, alerts and exposure data, and says what to do next.

AI assistant naming the most urgent incident and its next step

WHO IT IS FOR

Built for the people who have to respond

CISOs and IT leaders

A weekly, defensible answer to: what should we worry about, and what are we doing about it?

Small security teams

Analyst-grade prioritization without a dedicated threat intelligence function.

Executives and boards

A written summary of incidents, response times and open exposure, ready to download.

UNDER THE HOOD

Production-grade, even as a pilot

  • Isolated container on AWS. Runs on its own, behind a shared load balancer.
  • HTTPS only. Every connection is encrypted with a managed certificate.
  • Secrets in a vault. Keys live in AWS Secrets Manager, never in code.
  • Invented organization. The systems, alerts and incidents are sample data that reset on every restart; the threat feeds are real and public.

QUESTIONS

Before you ask

Is this a finished product?

It is a working pilot: a real application you can use, scoped to show the approach. A full engagement connects it to your own tools and data.

Does the demo use real data?

The threat intelligence is real and public, from sources such as CISA and abuse.ch. The organization, its systems, alerts and incidents are invented, and reset every time the pilot restarts.

How do I get into the live demo?

Request a demo and we will send sign-in details, or walk you through it on a short call.

Can it run inside our environment?

Yes. Every pilot is a self-contained container, so it can be deployed in your own cloud account or data center.

See ThreatReady against your own systems

A 30-minute walkthrough, with the questions that matter to your organization.